The Remote Job Had You Keep Company Laptops at Home. Now What?
A gig paid you to keep work laptops online at home, sit an interview or lend your ID. The FBI says that can feed a North Korean IT worker scheme. Steps now.
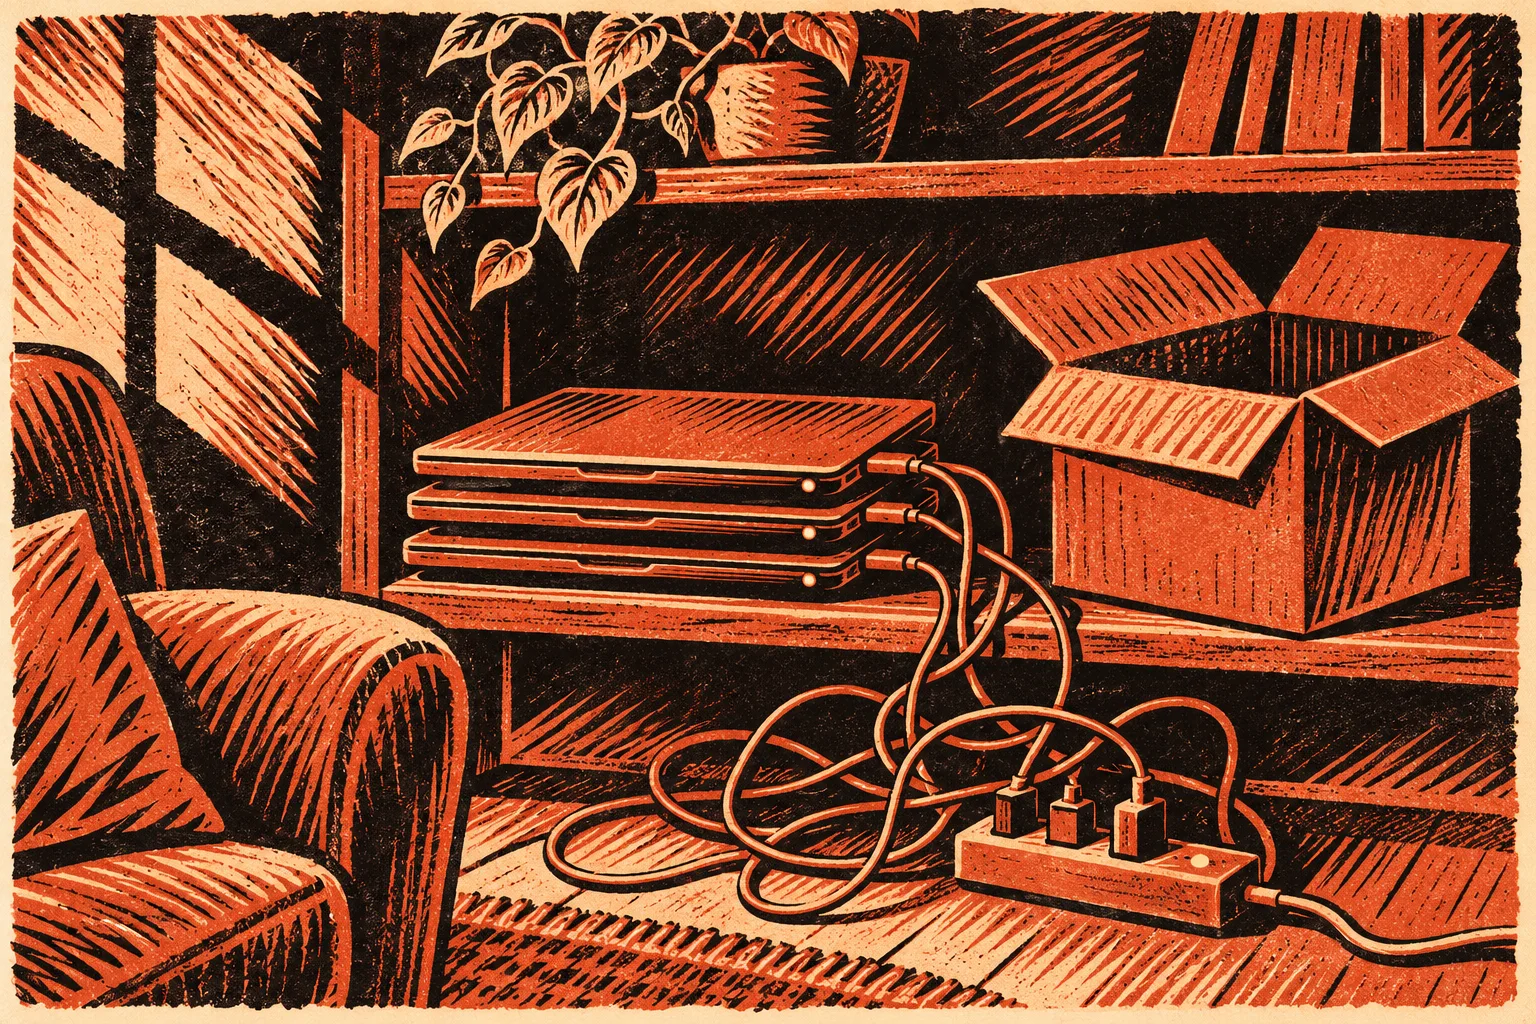
It looked like easy side income: plug in a few laptops a company shipped to you, keep them online, maybe join a video call under your own name. Then you read that the FBI calls this a “laptop farm.” If that describes your last few weeks or months, this page answers the questions people in your position ask first, and lays out how to report it and protect yourself.
On October 13, 2026, the FBI’s Internet Crime Complaint Center published public service announcement I-101326-PSA, “North Korean IT Workers Expanding Use of Facilitators, Broadening Recruitment.” It says North Korean IT workers post fake openings on well-known job boards, often as freelance gigs, asking for things like interviewing on someone’s behalf or receiving and hosting laptops at home. The FBI also says these recruiters strategically target people under financial stress. Being picked out that way is a reason the offer felt ordinary, not a sign that you did something foolish.
Is this what happened to me?
Compare what you were asked to do with the list in the FBI’s announcement. The PSA names these tasks:
- Hosting work laptops that stay connected to the internet at a personal residence.
- Appearing on camera, or taking interviews or meetings for someone else.
- Lending your identity, verifying someone else’s identity, or handing over access to social media or professional networking accounts.
- Shipping packages, completing urinalysis tests or submitting fingerprints.
The PSA also warns that some facilitators found their identities used without permission, or used to apply for more jobs than they had agreed to. If any of this sounds familiar, the rest of this page applies to you.
Why does it matter who was on the other end?
Because the companies that shipped those laptops thought they were hiring someone in the United States. A Justice Department press release of April 15, 2026 describes a case in which the identities of more than 80 U.S. people were used to obtain remote jobs at more than 100 U.S. companies. According to the release, a U.S.-based manager supervised at least five facilitators who hosted hundreds of company computers at their homes, and the scheme generated more than $5 million for the North Korean government.
That case involved people who, according to the department, knew what they were doing and were sentenced to 108 and 92 months in prison. Your situation may be very different. The FBI’s announcement says plainly that these activities are illegal and put people at risk of law enforcement scrutiny, which is why the steps below lean toward reporting early and getting advice, not toward quietly unplugging and hoping it goes away.
Do not accept more laptops, join more calls, or send anyone new documents or codes. Do not wipe, sell or ship the devices you already have unless law enforcement or a lawyer tells you what to do with them. They may be evidence, and they may also show how your identity was used.
What could each task have exposed?
Different tasks carry different risks for you. This table is a starting point for the conversation with a lawyer and with your own bank or credit bureaus.
| What you did | Why it matters | What to do about it |
|---|---|---|
| Kept company laptops online at home | Remote workers may have used your address and internet connection to appear to be in the U.S. | Leave the devices as they are and note when they arrived, who sent them and any shipping labels |
| Installed remote-access software or a hardware box on them | The PSA lists tools like AnyDesk, TeamViewer and KVM-over-IP devices as warning signs | Write down what was installed and on whose instructions. Do not remove it yourself |
| Joined interviews or meetings for someone | Your face and name may be attached to a job you never did | List the companies, dates and the platform used |
| Sent a copy of your ID or Social Security number | The PSA warns identities may be used for more jobs than agreed | Follow the recovery plan at IdentityTheft.gov and consider a credit freeze |
| Opened a bank account or received pay and passed money on | Money moving through you can draw scrutiny on its own | Keep every statement. Tell your lawyer before you talk to the bank about it |
| Gave your LinkedIn or other account login | Your profile may be messaging other recruits | Recover it using the FTC’s hacked account steps |
Do I need a lawyer?
It is worth talking to one before or while you report, especially if you were paid, received money for others, or let your name be used for a job. We cannot tell you how a prosecutor would see your case, and nothing here is legal advice. If cost is a worry, your state or local bar association can usually refer you to a lawyer, and legal aid organizations may help depending on your income. Bring the timeline described below.
How do I report it, and what should I include?
The FBI asks people to report to their local FBI field office and to file a complaint at IC3.gov. According to the PSA, useful details include:
- Street addresses linked to the activity, including your own if laptops were hosted there.
- Names, account usernames, phone numbers, email addresses, bank accounts and IP addresses you were given or saw.
- Any description or evidence of the people who directed you, such as chat logs, voice notes or payment records.
- Details about other facilitators or people involved, if you know of any.
Before you report, build a simple timeline: the job ad and where it ran, the first message, each device that arrived, each payment you received and each request you agreed to. Screenshots of the original listing are useful, because these ads are often removed.
What about my own identity and money?
The FTC’s job scams guide warns that if you gave personal information believing it was for payroll, you may now have an identity theft problem. Practical steps:
- Freeze your credit with Equifax, Experian and TransUnion. The FTC’s credit freeze guide says there is no cost to place or lift one, and you need to contact all three.
- Pull your reports at AnnualCreditReport.com and look for accounts or employers you do not recognize.
- If you receive a tax form from a company you never worked for, keep it. It may show where your identity was used.
- Change passwords on any account whose login you shared, and turn on two-factor authentication.
If the same “employer” also asked you to receive and forward boxes, our guide to reshipping jobs you already started covers that side. For spotting the next offer early, see checking a recruiter’s identity before an offer and our overview of fake remote job offers.
If you are being threatened
Some people try to step back and get pressure in return. The FBI’s announcement says these actors have used threats of violence, and have even hired U.S.-based facilitators to make in-person threats. If anyone threatens your life or physical safety, the PSA says to call 911. Save the messages, do not argue with the sender, and mention the threats when you file with the FBI. Stepping away from this is the right move, and you do not have to do it alone.
Sources
- FBI IC3, North Korean IT Workers Expanding Use of Facilitators, Broadening Recruitment (I-101326-PSA, October 13, 2026)
- U.S. Department of Justice, Two U.S. nationals sentenced for facilitating fraudulent remote IT worker scheme (April 15, 2026)
- FTC, Job Scams
- FTC, How to recover your hacked email or social media account
- FTC, What to know about credit freezes and fraud alerts
- FTC, IdentityTheft.gov
- FBI, Field Offices
Found a factual error or a source that has changed?
Send a correction →